Zyxel GS1900 office switches: the flaw behind attacks on 996 switches needs the newest firmware
 6 November 2026
Attackers took data from 996 Zyxel GS1900 office switches, 33 in the UK. The June firmware isn't enough; switches need Zyxel's Patch 3 build. Update today and change the switch's admin password.
What happened
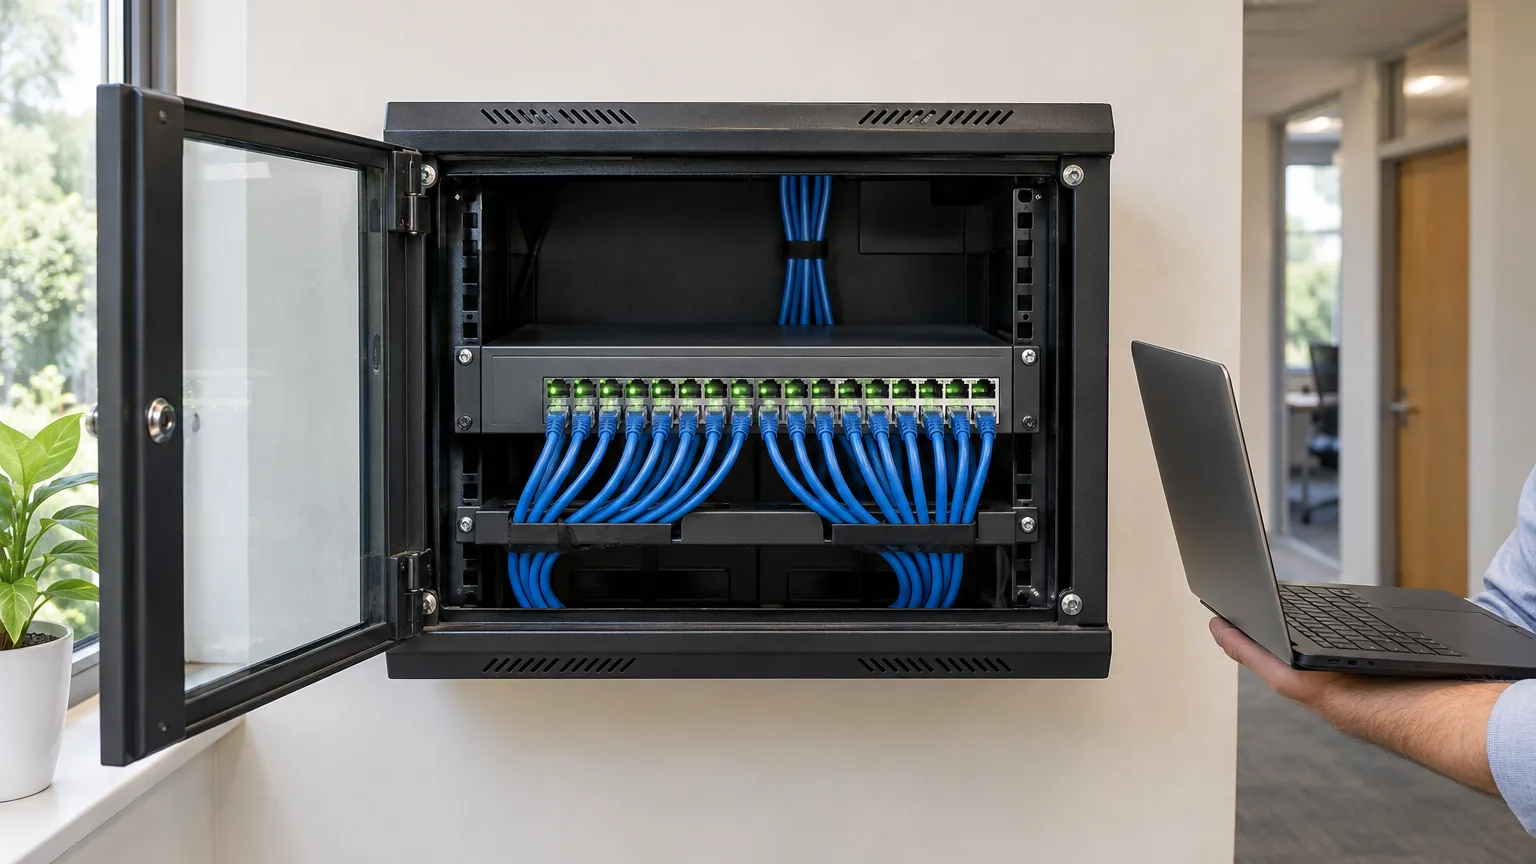
In September, security firm GreyNoise reported that attackers took settings, scrambled admin passwords and network details from 996 Zyxel GS1900 switches in 48 countries, 33 of them in the UK. It blamed a flaw Zyxel fixed in June. Binarly, the firm Zyxel credits with finding the new flaw, says the attackers' tool still works on that June update (its own advisory, and BleepingComputer, 04/11/2026). Zyxel's new firmware, called Patch 3, closes it.
Zyxel also fixed a separate flaw on 03/11/2026 in many of its Wi-Fi access points, the FWA7 mesh units and the USG LITE 60AX router, where someone on your network could take more control of the device than they should have.
Does this affect you
Offices with a Zyxel GS1900 switch, even one updated in June. The model name is on the label. Also offices with Zyxel NWA, WAX or WBE Wi-Fi access points, FWA7 units or a USG LITE 60AX router.
What to do
- Ask your IT person to put every GS1900 switch on the Patch 3 firmware for its model, for example 2.90(AAHL.3)C0 for the GS1900-24.
- Change the switch's admin password once it is updated. GreyNoise says 564 of the 996 still used the factory password, and the attackers took scrambled copies of admin passwords from the rest, so change it even if it is not the factory one. (That second point is our advice, based on what GreyNoise says was taken.)
- Check the switch's admin page can't be reached from the internet or guest Wi-Fi. Binarly says an attacker only needs to reach the switch's management service over the network, with no login.
- Update Zyxel access points and FWA7 units to the versions in Zyxel's table. The USG LITE 60AX gets V2.40(ACIP.0)C0 through the cloud, so check it has arrived.
Is it being attacked?
Yes. GreyNoise saw GS1900 switches attacked from about 17/08/2026 (report dated 21/09/2026). Zyxel's advisory doesn't mention attacks. No attacks are reported on the access point flaw.
Found by
Zyxel credits Yegor Vasilenko and Fernando Mercès of Binarly for the switch flaw, and Jinpyo Lee for the access point flaw. Neither advisory mentions Ai. Tag: people.
For developers
- CVE-2026-107441 (CVSS 3.1 8.8, Zyxel, AV:A/AC:L/PR:N/UI:N): out-of-bounds write in the CGI program of GS1900 firmware; unauthenticated LAN attacker, potential OS command execution via a crafted HTTP request. Affected 2.90(xxxx.2)C0 and earlier, fixed 2.90(xxxx.3)C0: GS1900-8 AAHH, -8HP AAHI, -10HP AAZI, -16 AAHJ, -24 AAHL, -24E AAHK, -24EP ABTO, -24HPv2 ABTP, -48 AAHN, -48HPv2 ABTQ. The .2 builds are the June fix for CVE-2026-7273, so June-patched switches are inside the affected range.
- Binarly (advisory BRLY-2026-057, 03/11/2026, read in full on 07/11/2026): the request parameter table holds "140 entries of 1024 bytes each" and is followed by the global parameter counter, so an overrun corrupts the counter before the Patch 2 count check runs; Patch 3 checks the count first and limits parameter size. Binarly scores it CVSS 3.1 9.8 (AV:N); Zyxel scores it 8.8 (AV:A). Binarly says the exploit recovered from the attackers' server matches the one it analysed, and that all ten June releases remain affected. BleepingComputer (04/11/2026) reports Binarly told Zyxel on 29/09/2026.
- GreyNoise (21/09/2026): PyArmor-obfuscated Python exploit, TFTP fetch of a collector script, data staged at /home/web/tmp/info.txt; actor "same or related to" Acronis's Red Heron. IoCs in GreyNoise's report include *.981666.xyz (C2), 104.225.153.141 (C2) and 74.48.66.73 (staging). Neither GreyNoise nor Binarly says which firmware the attacked switches ran.
- KEV: CVE-2026-7273 added 21/09/2026 (due 24/09/2026). CVE-2026-107441 not in the catalogue released 06/11/2026 (2026.11.06, checked 07/11/2026), and CISA's enrichment on its CVE record (03/11/2026) marks Exploitation as none.
- CVE-2026-76955 (CVSS 3.1 8.8, Zyxel): buffer overflow in the zdp_wtp binary on APs, FWA7 and USG LITE 60AX; LAN-based privilege escalation; no exploitation reported. AP lines on 7.12 move to the next .1 build (for example NWA110AX 7.12(ABTG.1)C0), 7.40 lines to the next .2 build (for example NWA50BE 7.40(ACPB.2)C0); FWA7 Leaf Plus, Root and Root Plus 7.40 .2 builds; WAC500H 6.70(ABWA.7)C0 and earlier, hotfix on request; USG LITE 60AX V2.00(ACIP.0)C0 to V2.30(ACIP.1)C0 affected, V2.40(ACIP.0)C0 by cloud. Zyxel says on-market products not listed are not affected; models past their vulnerability support period aren't patched.
Sources
- Zyxel advisory, GS1900 switches, 03/11/2026
- Zyxel Community, GS1900 V2.90 Patch 3 release notes, October 2026
- Binarly advisory BRLY-2026-057, 03/11/2026
- GreyNoise, Open Season on Kapibala, 21/09/2026
- CISA KEV JSON catalogue 2026.11.06
- CVE.org, CVE-2026-107441
- Zyxel advisory, APs, FWA7 and Security Routers, 03/11/2026
- BleepingComputer, 04/11/2026, for the date Binarly told Zyxel
Read next
More from The Patch Wave
- Act today
iPhones, iPads and Macs: update today, Apple has patched a compression flaw already on the US exploited list
Apple's 09/11/2026 updates fix the Brotli flaw CVE-2026-111497, which CISA added to its exploited list on 27/10/2026, and an iMessage group chat flaw. Update iPhones, iPads and Macs today.
- Act today
Microsoft Outlook: November's updates fix a flaw attackers are already using
Microsoft says attackers are already using an Outlook flaw (CVE-2026-124194) fixed in this month's updates. Update Office and run Windows Update today.
- Watch
Hotmail and Outlook.com bounced some business email for nearly three days: Microsoft has fixed it
Microsoft says a faulty spam rule update made Outlook.com, Hotmail and Live wrongly block some email from 06/11 to 09/11/2026. It has rolled the update back. If your mail to those addresses still bounces, tell your IT person.